1. One-step Payments
Kushki Docs
English
  • Español
  • English
  • Home
  • Quick Start
    • Frequently Asked Questions
    • Moving to Production
    • Policy for Important API Changes
    • Test Data
    • Error Codes
    • Latest Features
  • Payment Glossary
    • Payments Glossary
  • One-time card payments (Online)
    • Supported card brands
    • Functionalities by business model
    • Network Tokens
    • One-step Payments
      • How do Card Payments Work?
      • Accept a Card Payment
      • Direct charge (without token)
      • Accept One-Time Payments with OTP
      • OTP Authentication Error Codes
      • Error codes for single card payments
    • Two-steps Payments
      • How do one-time payments with authorization and capture work?
      • Receive payments with authorization and capture
    • Refunds
      • Returns, cancellations, and refunds
    • 3DS Authentication
      • Introduction to 3DS
      • 3DS API integration
      • 3DS integration with kushki.js library
      • 3DS API integration plus kushki.js library
      • 3DS Error Codes
    • Apple Pay Payments
      • Apple Pay Configuration
      • Apple Pay Sandbox testing
  • Recurring Card Payments (Online)
    • Functionalities by business model
    • External subscriptions to Kushki
    • Authenticate your subscriptions with 3DS
    • Accept one-click payments with 3DS
    • Error codes in recurring charges
    • Apple Pay for Subscriptions
    • Scheduled payments
      • How do Credit or Debit Card Payment Recurring Charges Work?
      • Create a recurring charge
      • Manage your Scheduled Charges
    • OneClick Payments
      • Accepting One-Click Payments
      • How does authorization and capture work in OneClick payments?
      • Receive OneClick payments with authorization and capture
  • Card-present payments
    • Accept card present payments
    • Test data
    • Webhooks for card present
    • Raw card-present API
      • Raw card-present API overview
      • Cryptographic key exchange
      • Sample script to encrypt information
      • Take Payments
      • Frequently Asked Questions
      • Error codes for card-present transactions
    • Transactions
      • Transactions
      • Cancel payments
    • Kushki One
      • First Steps
      • Autenticación y Cifrado de Requests
      • Accept payments with Kushki One
      • Amount Format
      • Async services and webhooks
      • Printing on SmartPOS terminal
      • Unified Error Catalog — Kushki ONE Connect
    • Kushki One Payment App
      • Overview
      • Process a payment
      • Split payment on the terminal
      • Refunds and PreAuth & Capture
      • Review Your Transactions
      • Terminal Setup
  • Wire Transfers
    • Shopping experiences and transaction details for bank transfer payments
    • Receive Wire Transfers
    • Check the Status of a Transaction
  • Cash Payments
    • Accept a Cash Payment
    • Authorized locations
    • Error Codes for declined cash transaction
  • Alternative payment methods (APM)
    • How do APM payments work?
    • Accept Yape payments
  • Money Disbursement
    • Wire Transfer
      • How does the disbursement through bank transfer work?
      • Payment disbursement to bank accounts
      • Error codes for transfer disbursements
    • Card
      • How does sending funds to cards work?
      • Send money to a card
      • Error Codes
  • Plugins
    • Shopify
      • Shopify
      • Plugin Operation
    • VTEX
      • VTEX Integration Guide
  • Payment Links
    • Smartlinks
  • Payment forms and buttons
    • Kajita
      • How Does it Work?
      • Payment Kajitas
    • Payment Button
      • Overview
      • Generate a payment button
  • Branch Offices Management
    • How to Onboard Submerchants via API
  • Notifications
    • Good Practices
    • Check your Webhooks
    • One-time Payments Webhooks
      • Webhook for One-Time Payments made with a card
      • Webhook for One-Time Payments by Wire Transfer
      • Webhook for One-Time Payments in Cash
    • Recurring Payments Webhooks
      • Webhook for Recurring Payments Made with Card
    • Payment Distribution Webhooks
      • Webhook for payment disbursement through wire transfer
      • Webhook for card disbursement
    • Payment button Webhooks
      • Webhooks with Payment Button
    • Smartlinks Webhooks
      • Webhooks with Smartlinks
    • Refunds Webhooks
      • Webhook for Voids and Refunds
      • Chargeback Webhooks
HomeMexico 🇲🇽Ecuador 🇪🇨Chile 🇨🇱Colombia 🇨🇴Peru 🇵🇪
Status
Soporte / Support
English
  • Español
  • English
  1. One-step Payments

Accept One-Time Payments with OTP

OTP (One Time Password) is another layer of online protection against financial fraud.
This functionality is available for the following models:
☑ Acquirer

☑ Aggregator
Please contact us to activate OTP in your merchant.
A "one-time password" (OTP) authentication (also known as dynamic password) is a password that is valid for a single transaction. It aims to reduce fraud and provide extra security for your merchant's online payments.
Consider using OTP when your merchant has a substantial amount of fraud or particularly sensitive or high-value transactions since this might result in a lower conversion due to added steps in the payment process.
You will be able to specify the type of transactions for which OTP validation will be requested, for example, when the transaction amount exceeds a certain threshold.
This feature is only available for Web integrations in one-time card payments.
Check below for the availability of OTP authentication with the affiliation and integration models available in Kushki.

OTP authentication availability#

By affiliation methods#

OTP authentication is available when processing transactions with the following card brands:

Aggregation and acquiring#

Credit card and debit card#
VISAMasterCard
Supported ✅Supported ✅

By integration methods#

OTP authentication is available in the following integration methods:
Supported ✅Not supported ❌
Integration with ShopifyiOS integration (SDK)
Integration with Adobe CommerceAndroid integration (SDK)
Integration with Smartlink
Integration with Kajita
Integration with payment button
Integration through API
Kushki.js integration
Kushki.js Hosted Fields integration
To keep in mind
Due to our risk policies, the available payment methods and the integration type may vary once you complete the affiliation. We will tell you how to proceed if this process applies to your merchant.
An example of what you will integrate is shown below:

How does it work?#

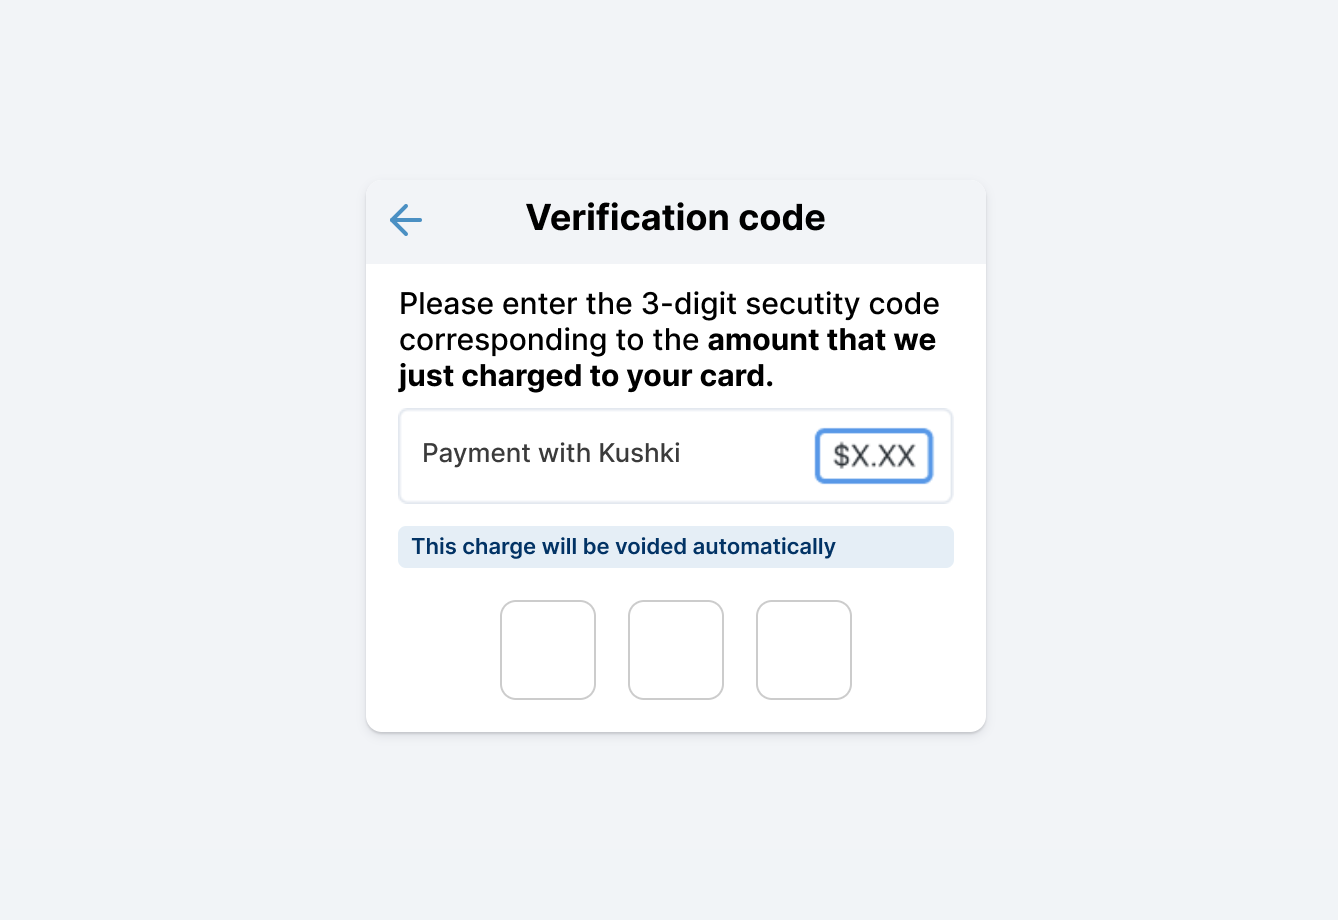
After the user completes the form and clicks on the payment button, a small charge of a random three-digit amount will be made to the user's card (between 1.86 and 6.99 PEN). The amount charged must be entered by the user to authenticate the transaction. The user will typically be able to verify this amount in their account transactions or through their bank's alert and notifications service, if available. This charge will be automatically canceled in a couple of minutes.
Once the payer consults the amount charged, they must enter this number in an interface that will be shown to your users to validate the transaction. The following is an example of the interface and the message you can present to capture the validation amount:
OTP
To keep in mind
The OTP expires after 10 minutes.
The user will have 3 attempts to enter a valid OTP. In case all attempts are wrong, the OTP will be approved on the third attempt (even if the data entered is incorrect), in this way the rejection will be associated with the charge request. Normally with the rejection code K322 and the subcode K326.

1. Set up your Front-end#

Set up your front-end according to your integration.

Kajita#

Follow our instructions for Kajita described in our guide to accept card payments.
Once you set up OTP for your merchant, Kajita will automatically ask for the OTP in each payment attempt. You don't need to do anything else.

Kushki.js#

Follow our instructions for Kushki.js described in our guide to accept card payments.
Now, before sending the data to the end-point in your back-end, we must collect the OTP from the user and validate it.
When an OTP is enabled, the response obtained from the requestToken() method will be as shown below:
Once the requestToken() response is obtained, you will need to display a field in your form to collect the user's OTP.
By using the OTP collected the user along with the secureId obtained from requestToken, you must run the requestSecureServiceValidation() method to authenticate the OTP and obtain the code to send it to your back-end.

Kushki.js Hosted Fields#

If you need to validate the OTP code, you can use the onOTPValidation() method on your card instance. It is executed when a value is entered in the OTP field to validate the code. This method returns three callbacks (onSuccess, onError and onRequired), which will allow you to identify the status of the OTP validation in the hosted fields.
To implement OTP validation, first add a div container with id otp_id inside your application to display the field for entering the OTP value.
Note: The request for OTP validation will be triggered automatically by entering 3 digits in the field.
Second, you need to reference the otp_id container within your CardOptions instance.
Finally, call the onOTPValidation() method which will indicate whether or not it is necessary to perform the validation through a callback (onSuccess, onError or onRequired). If validation is required, the field with the id otp_id will be displayed for the user to enter the required information.
Learn more about OTP validation with Kushki.js Hosted Fields.

2. Set up your Back-end#

Please follow the instructions in our guide to accept card payments.

3. Test your Integration#

You may use test cards in test mode to ensure that your integration is ready. Use them with any CVV and a future expiration date.
Approved transaction: 5451951574925480
Declined transaction during token request (front-end): 4574441215190335
Declined transaction in OTP charge request (front-end): 4349003000047015
OTP validation amount: 155

4. Prepare your Certification#

Follow the guidelines described in our guide to accept card payments.
In addition to the guidelines described in the guide, if you are using Kushki.js, you also need to validate the following:
There is a message explaining OTP.
The OTP field appears when clicking on pay.
The OTP field must be required.
The OTP field only accepts numbers.
The OTP field allows exactly 3 digits.
Kushki's logo must be visible for the customer. You can find our logo in several formats here.

Modificado en 2026-10-14 19:58:22
Anterior
Direct charge (without token)
Siguiente
OTP Authentication Error Codes
Built with